KeeneticOS 5.2
KeeneticOS release notes for Keenetic Buddy 6 (KN-3411) in the Preview Channel
KeeneticOS releases in this channel provide the chance to be among the first to try the latest updates, performance improvements and new features, all with minimal risk. It is updated roughly every two weeks, with major updates about every two months. Releases here are typically more than a month in advance of release to the general audience in the Main Channel.
Keenetic Buddy 6 (KN-3411) is currently in the Standard Updates support period and receives regular software updates, including security enhancements, new features, operating system updates, and bug fixes.
KeeneticOS 5.2 Beta 3
05/11/2026
New
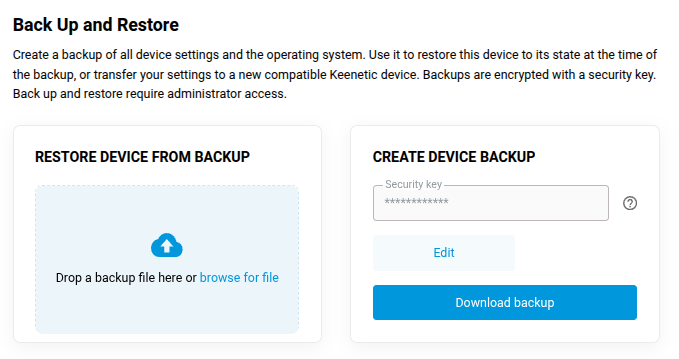
Implemented system backup creation and deployment. [NDM-4830]
system backup password generate— generate a security key for the backup file;system backup password set {password}— set a{password}security key to be used for creating a backup file;system backup password no set— clear the configured backup security key;system backup password validate {password}— validate the strength of a{password}security key;system backup commit— commit the deployed backup using configuration only and restart the device;system backup reset— reset the backup state and cancel current deployment;show system backup status— display the status of the currently deployed backup;copy flash:/backup {destination}— create a backup image containing device configuration and operating system at the specified{destination};copy {source} flash:/backup {password}— deploy an existing backup image from the specified{source}using the{password}security key.
Added a Back Up and Restore section on the Files tab in System Settings to manage encrypted backups of all device settings and the operating system. Backups can be used to restore your device to its previous state or to transfer your settings to another compatible device. [NWI-5129]
Improved
Security enhancements.
Fixed use-after-free vulnerability CVE-2026-98432 in IPv4 TCP socket option cleanup. [SYS-1930]
Updated the MediaTek wireless driver to address multiple vulnerabilities, including CVE-2026-68603, CVE-2026-68624 and CVE-2026-79062. [SYS-1920]
Addressed a vulnerability in the Wi-Fi bridge handler that could cause denial of service when exploited from the local network. [NDM-4826]
Improved authentication handling and isolation to prevent username enumeration and resource blocking under concurrent authentication attempts. [NDM-4653]
Fixed
The following fixes have been applied to the Web Interface.
Corrected operation of administrative controls for read-only users to prevent permission errors on attempted actions. [NWI-5169]
Corrected the hint button indent in the Roaming for Wireless Clients section on the Wi-Fi Network Settings pop-up. [NWI-5168]
Fixed guest Wi-Fi network propagation over Wi-Fi System extenders after Controller restart. [NDM-4846]
Corrected DHCP RELEASE and RENEW message addressing to
unicastover wireless networks. [SYS-1903]
KeeneticOS 5.2 Beta 2
27/10/2026
Improved
Upgraded the ca-certificates package to blacklist unsafe root certificates, including
emSign ECC Root CA - G3andComodo AAA Services root. [SYS-1918]Improved the Web Interface authentication procedure for users without administrator privileges. [NDM-4782]
Refined the command restrictions for read-only users, preventing privilege escalation via program execution. [NDM-4773]
Refined SSH access validation to eliminate spurious SFTP access denial messages. [NDM-4790]
Fixed
The following fixes have been applied to the Web Interface.
Corrected false detection of SAE-EXT protection in the Wi-Fi System. [NWI-5158]
Fixed the display and download operation for the Security log file on the System Settings page. [NWI-5140]
KeeneticOS 5.2 Beta 1
19/10/2026
New
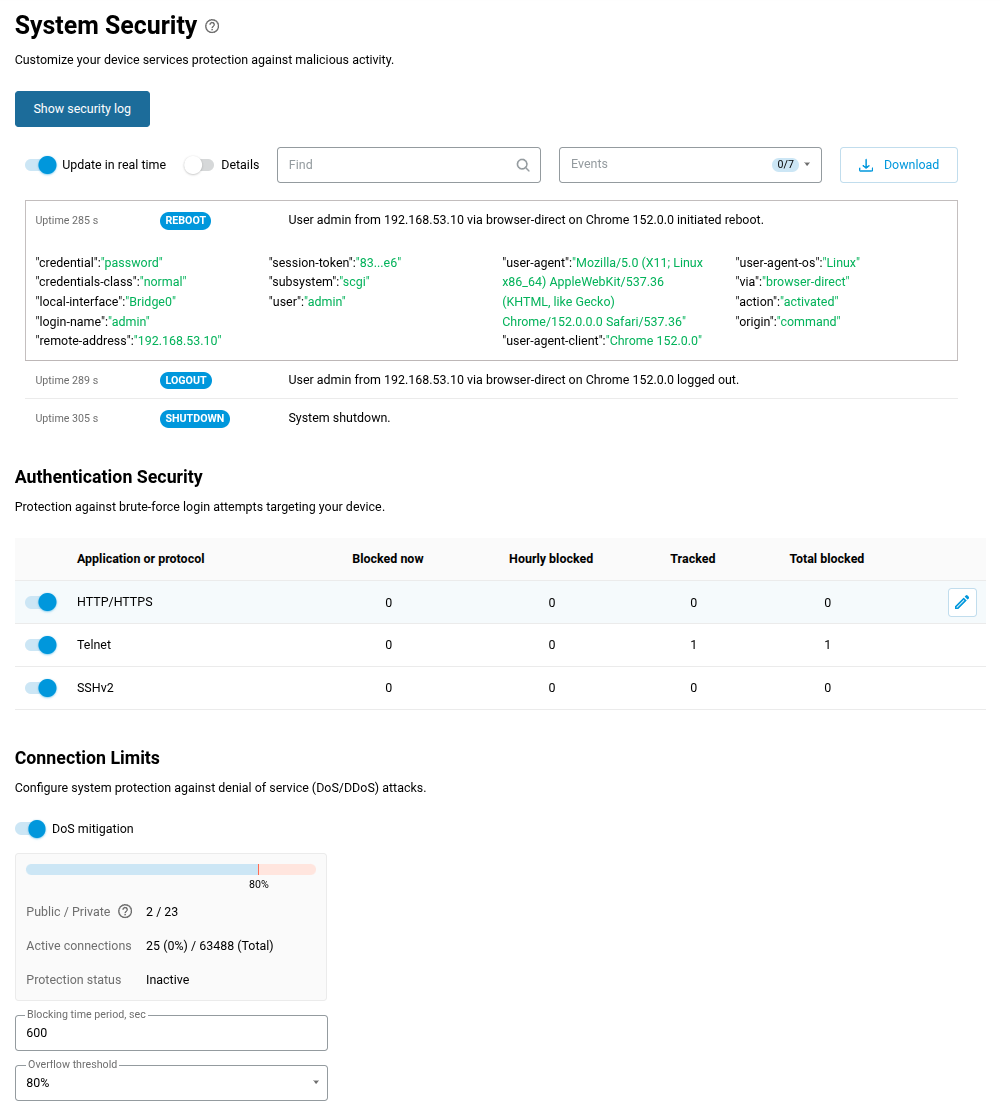
Added System Security page featuring a display of system events in the Security Log, brute-force protection settings for network services, and DoS attack mitigation controls. [NWI-5104]
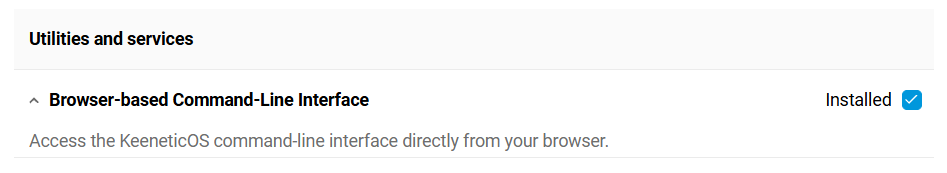
Implemented the web-based command line system shell, accessible from the right slide-out menu after installing the Browser-based Command-Line Interface system component. [NWI-4900]

Improved
Upgraded the OpenSSL library to version 3.5.9 to address multiple vulnerabilities, including CVE-2026-35189, CVE-2026-54872, CVE-2026-72897, CVE-2026-75806, CVE-2026-84782, and CVE-2026-84783. [NDM-4754]
Upgraded the nginx application to version 1.30.6 to address multiple vulnerabilities, including CVE-2026-15176, CVE-2026-93479, CVE-2026-97205, and CVE-2026-97629. [NDM-4769]
Refined the deletion procedure and improved backward compatibility when configuring Wi-Fi networks. [NDM-4711]
Upgraded the libxml2 library to version 2.15.4, resolving the following security issues: CVE-2026-86137, CVE-2026-86138, CVE-2026-86139, CVE-2026-86140, CVE-2026-86141, CVE-2026-86142, CVE-2026-86143, and CVE-2026-86144. [NDM-4676]
The following improvements have been applied to the Web Interface.
Improved the Keenetic Domain Name section with an option to change the registered name for the device. [NWI-5065]
Improved the display of longer texts by implementing line breaks based on syllables. [NWI-5074]
Updated SSL/TLS cipher suite configuration and added ML-KEM support for post-quantum cryptography. [NDM-4663]
The following improvements have been applied to the Web Interface.
Enhanced the Clients page on Extender devices by adding an option to hide offline clients and a tooltip to display the client count by status. [NWI-5051]
Enhanced the brute-force lockout policy command set. [NDM-4655]
ip [http|telnet|ssh] lockout-policy (enable | threshold {thr} | duration {dur} | observation-window {wnd})— set up the lockout policy for device management sessions;show ip [http|telnet|ssh] lockout-policy— display the lockout details for device management sessions.
Upgraded the libwebsockets library to version 4.5.8, mitigating the CVE-2025-11678, CVE-2025-11679, and CVE-2025-11680 vulnerabilities. [NDM-4622]
Upgraded the system authentication method for the HTTP suite to harden security. [NDM-4515]
Enabled post-quantum key exchange for the SSH protocol to comply with modern security standard. [NDM-4299]
The following improvements have been applied to the Web Interface.
Added access tokens information display on the Users and Access page. [NWI-4923]

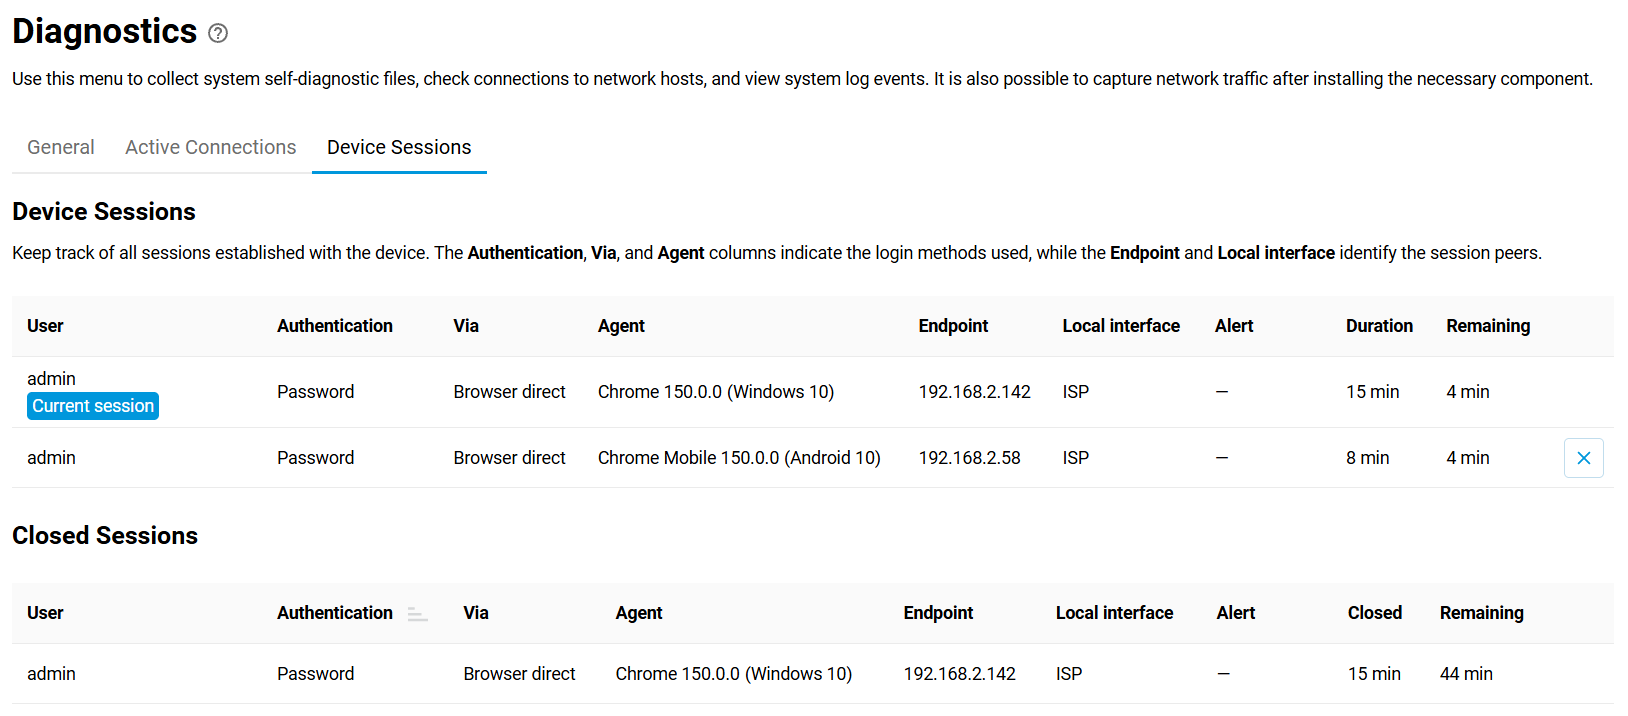
Added a dedicated tab on the Diagnostics page showing system sessions information. [NWI-4924]
Improved the Wireless Access Control page operation when no changes are made to access list. [SYS-1808]
Enabled the inclusion of segments without an IP address on the controller node in the Wi-Fi System. [NDM-4443]
Fixed
The following fixes have been applied to the Web Interface.
Corrected the background colour for the Wi-Fi Monitor chart when using the Dark theme. [NWI-5135]
Fixed the wireless network reconnection failure that occurred on iOS and other client types after restarting the Wi-Fi System controller. [SYS-1844]